
Everyone sees only what they are authorized for; every action leaves a trace.
The principles of information security management systems are built into the design: least privilege, confidentiality classes, activity logging and data sovereignty.
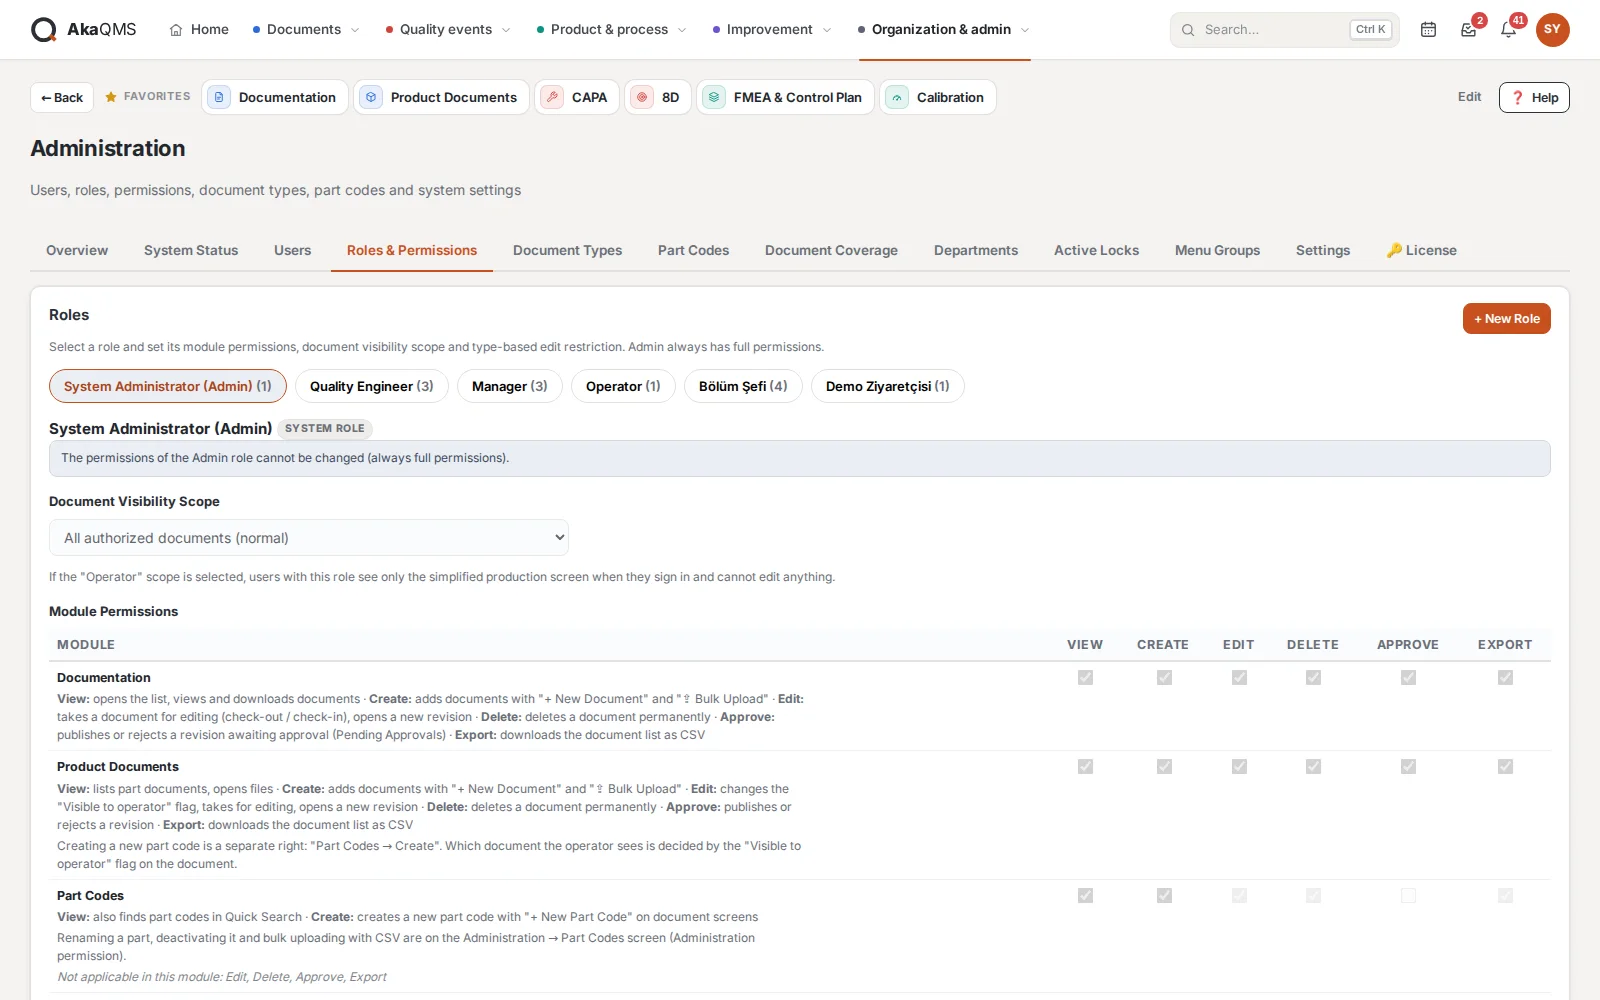
Role and permission matrix
Six rights per module: view, create, edit, approve, delete, export. Built-in roles can be changed and new roles created.
- Only authorized modules in the menuUsers do not see modules they have no permission for in the menu, and the server rejects the request too.
- Restrictions per documentPublic / Internal / Confidential classes; a document can be opened only to selected roles and people if needed. A role can be limited to editing certain document types only.
- Operator scopeOperator accounts see only the production screen and the documents opened to them.
- Two conditions for approvalIn modules such as MSA and SPC, approval requires both approval rights in the role and being assigned to the record; nobody can approve their own revision.
Logging, passwords, connections.
Activity log
Sign-in, viewing, download, save, approval, permission and license changes. Each row has the user, IP, date and time and a content hash; presented to the auditor as CSV or PDF.
Password policy
Password change at first sign-in; a temporary lock after five failed attempts; optional 90-day renewal; the last three passwords cannot be reused; the session closes after three hours of inactivity.
No data before sign-in
The sign-in screen shows no records; a session closes by itself after a period of inactivity.
Web protections
A security header is required on every state-changing request; CSRF, XSS and path traversal protections are standard. Encrypted connections (HTTPS) can be turned on.
Data stays in the company
The application does not connect to the internet or send data to external services. The license is validated offline, inside the server.
Confidential amounts
In the Performance module, bonus amounts are shown only to authorized people and are not even written to the activity log.
TISAX · ISO 27001AkaQMS is designed in line with the principles of these standards; this is not a certification. Certification is your company's own process; AkaQMS provides the records, permissions and confidentiality framework that process asks for.
Does your IT team have questions?
Let's go through installation, network and backup details with your technical team.